
Dropbox breach via Lenovo ID affected 5,000 accounts
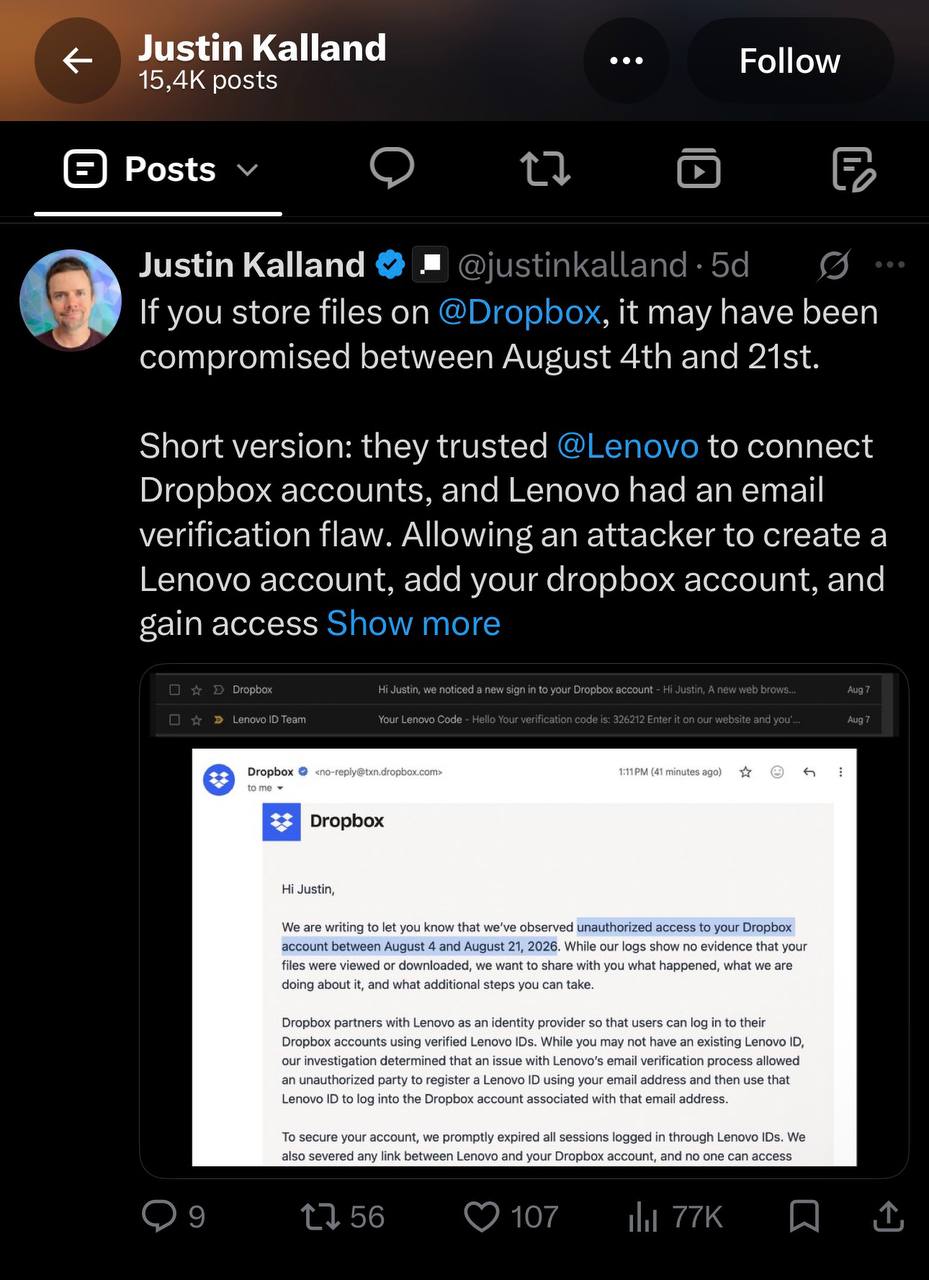
In August, hackers compromised about 5,000 Dropbox accounts. The cloud service itself was not directly attacked—the intruders used login via Lenovo ID, an account for accessing Lenovo products. The incident affected users who had not enabled multi-factor authentication.
The attack scheme was notable: a flaw was found in the email verification mechanism during Lenovo ID registration. It allowed creating accounts using other people’s email addresses, even if the owners of those addresses had never registered with Lenovo. Lenovo IDs created this way were then used to log into Dropbox accounts.
For about a third of compromised records, attackers actually viewed or downloaded files. For the rest, no evidence of access to content was found. Dropbox began blocking affected accounts after discovering the issue and notified users and regulators.
Some Dropbox owners received warnings on August 31. In them, the company indicated that unauthorized access was recorded from August 4 to August 21. Some users were informed about file viewing and downloading, while others were told that no signs of access to the content were found.
Lenovo acknowledged the existence of an old integration between Lenovo ID and Dropbox that could incorrectly verify some accounts. The companies are jointly working to resolve the issue. Lenovo specifically clarified that its own clients were not affected by the incident.
The incident shows that hacking does not always require breaking the cloud service’s own protection. An error in the linkage between platforms combined with the lack of multi-factor authentication made the attackers’ task noticeably easier. According to Bloomberg, Dropbox shares fell to 6.6% in over-the-counter trading on September 1.
Primary source: cisoclub.ru ↗