A RingRTC vulnerability could have prevented Signal calls from ending
XORit Editorial · Sources, AI assistance and corrections
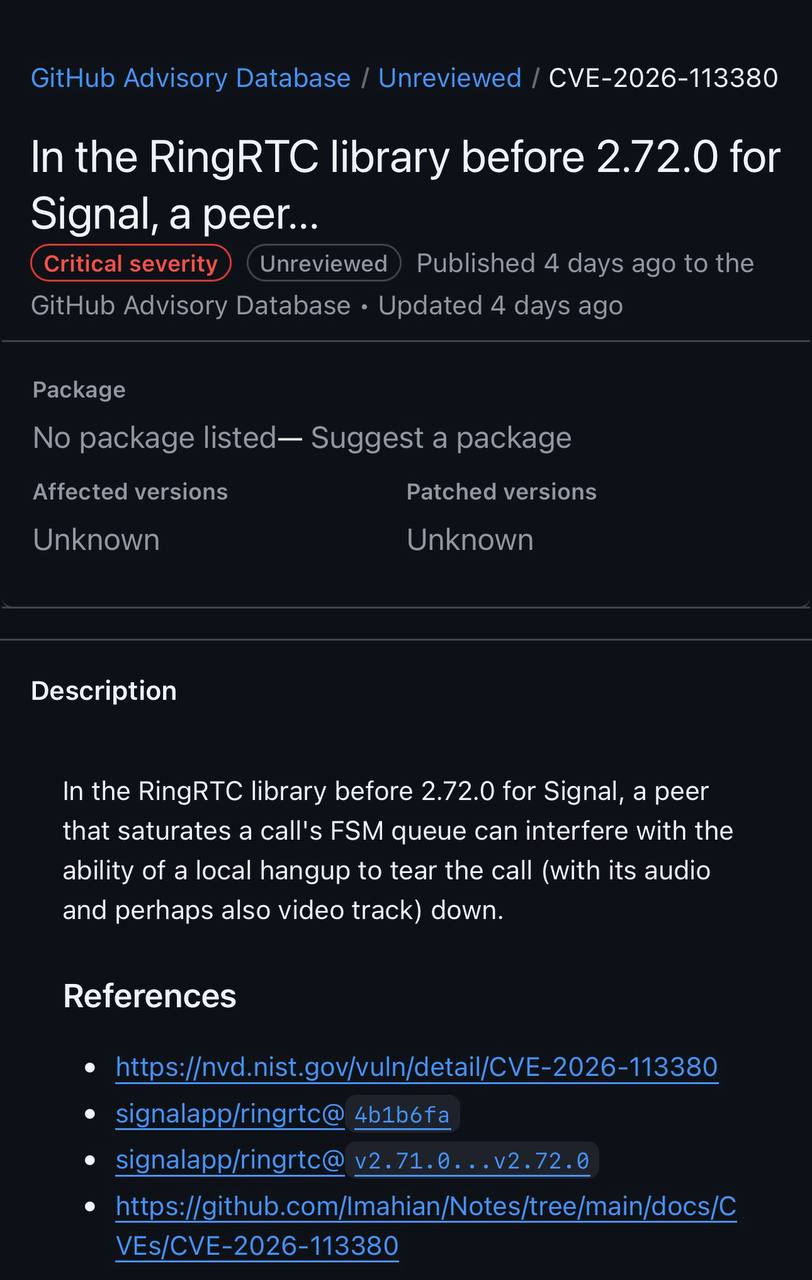
In Signal’s RingRTC library, a remote participant could saturate the call finite-state machine (FSM) queue in versions before 2.72.0. This could have prevented a call from ending on the user’s device.
According to the GitHub Advisory Database description, in such a failure the call might not end along with its audio track and possibly its video track. The vulnerability received a CVSS 4.0 score of 9.3 out of 10. The advisory was published on October 20, 2026; it lists the affected and patched versions as unknown.
Translation editors: Соловьев В., Пеков А.
Source: github.com ↗